

How well is your company secured?
Independent security reviews for manufacturing, critical infrastructure and mid-sized companies. On site across Germany, performed by OffSec-certified penetration testers.
Book a call- OSCP
- OSWE
- OSEP
- Covert Access Specialist
- BHE security concepts (KRITIS)
Your business keeps evolving. Does your security technology?
Fence, access control, cameras, visitor badges: everything worked at handover. Since then staff, routines and habits have moved on. Whether the technology still protects the way it was meant to is only shown by someone who actually wants to get in.
That is what we do. We take an attacker’s route, from the car park to the control cabinet, and find the inconspicuous spots where everyday oversights undo your measures. That puts your security to the test today and leaves you time to fix things.
Planning to invest in security technology? Then the review is your baseline. It shows where your money has the greatest effect and where an organisational change is enough.
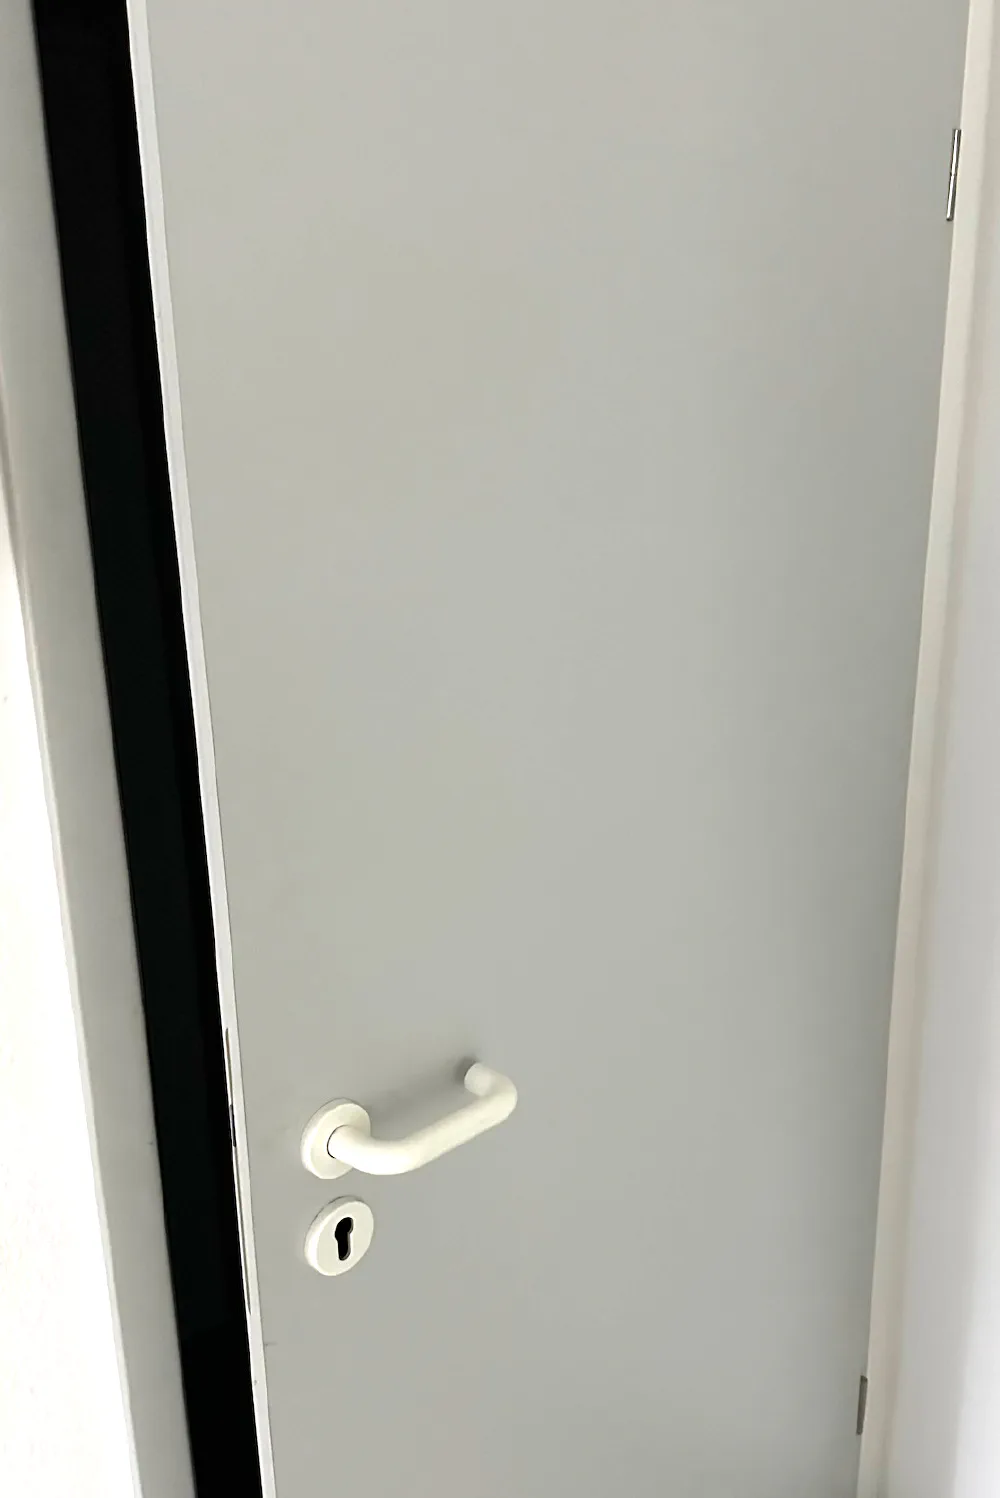
The server room door stood open during working hours. After hours the floor is secured; during the day everything depends on this one door.
- Effort: low
- Priority: immediate
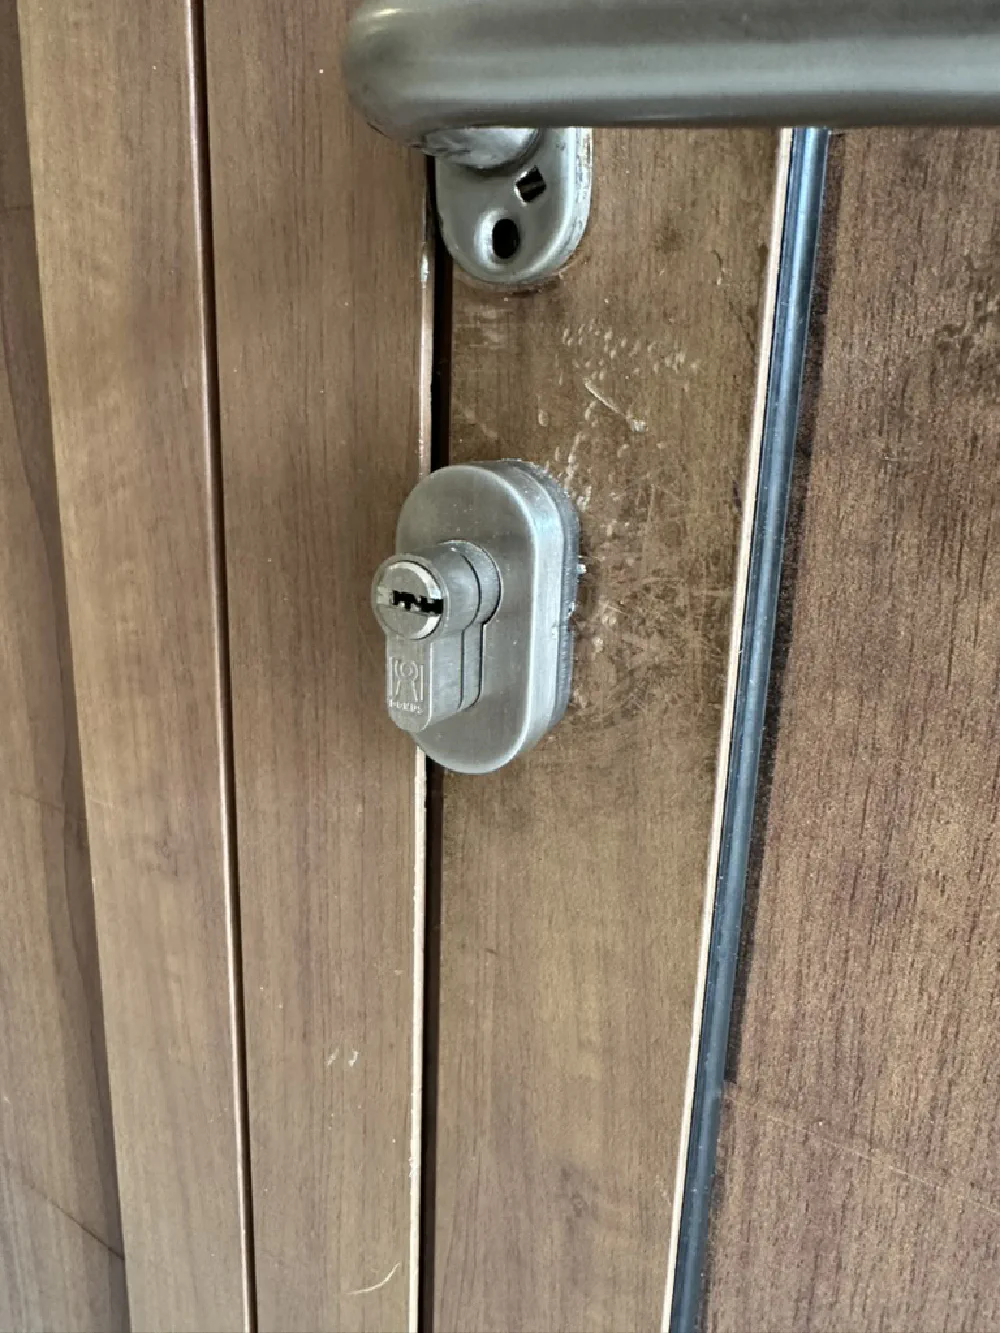
The cylinder protrudes and its anti-pull protection is exposed. A well-known weak point, fixed with a correctly sized cylinder.
- Effort: low
- Priority: immediate
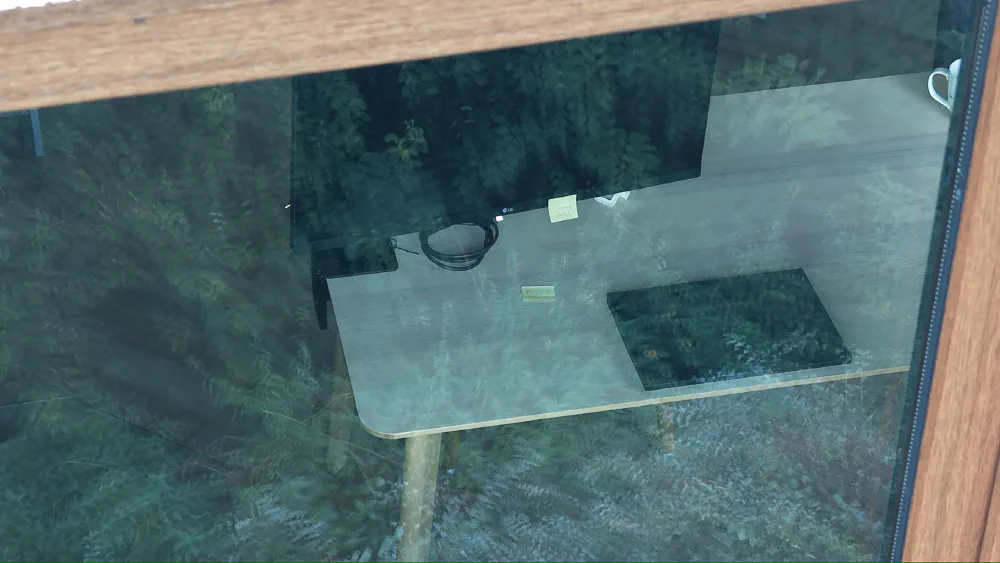
Upper floor, a workstation behind the window. Readable through the glass, here captured by drone: a note with a login password is stuck to the monitor.
- Effort: low
- Priority: immediate
Industry & Critical Infrastructure
- You have
- Site security, access control and segmented OT networks.
- We test
- Whether they stop an intruder: from the gate across the shop floor to the control cabinet.
- Production, PLCs and OT access points
- Hybrid attack paths from physical to IT
- Report with photos and priorities
From 1 day on site, quote by scope
Offices, Practices & Law Firms
- You have
- A locking system, an alarm and a reception desk.
- We test
- Whether they protect files, server room and visitor flow, in one day.
- Reception, files and IT area
- Evidence of GDPR due diligence
- Report with photos and priorities
from
€990 net
ISO 27001 & NIS2
- You have
- Your physical controls documented.
- We test
- Whether they work, with effectiveness evidence per control for audit and certification.
- Physical controls from Annex A
- Evidence for clause 9.1
- NIS2 risk management
Quote by scope
How a review works
Minimal effort for you, clear findings for your security
Brief call
30-45 min.We get to know your site: what you make, what must not stop, where the data lives. Scope and quote follow from that.
Order & rules
in writingWritten order and rules of engagement: limits, time windows, contacts, emergency contact. No signature, no test.
On-site test
4 hrs - 3 daysGrounds, building, access and locking systems, with minimal disruption to your operations
Report
Within 5 daysExecutive summary, photos and evidence, prioritized recommendations (quick wins / medium-term / investment)
Debrief
30-60 min.Review the action plan together, set priorities, plan next steps
What we test
Request an audit
Grounds & perimeter
Fences, gates, lighting, cameras. We test whether your perimeter actually keeps intruders out and detects attempts to get in.

Access & locking
Badges, locking systems, biometrics, visitor handling. We test whether outsiders stay outside, even when someone holds the door.

Production, OT & server rooms
Control cabinets, maintenance access, network sockets, server rooms. We test whether access to machines and data is protected the way you expect.

Reception & staff
Visitor traffic, supplier entrances, unknown people on the shop floor. We test whether your team challenges strangers and reports anything unusual.
From the field: few fixes, big effect
A mid-sized manufacturer with personal data and several production lines. Solid doors, cameras and a properly set up Wi-Fi were in place.
Still, one route led from a ground-floor window through an open network socket to the backups of the central directory. Five of the eight findings were high or critical. The most effective immediate measures cost almost nothing: close the door, remove the key, authenticate backup access, segment the network.
- 8
- findings
- 5
- of them high or critical
- 5
- low-cost immediate fixes
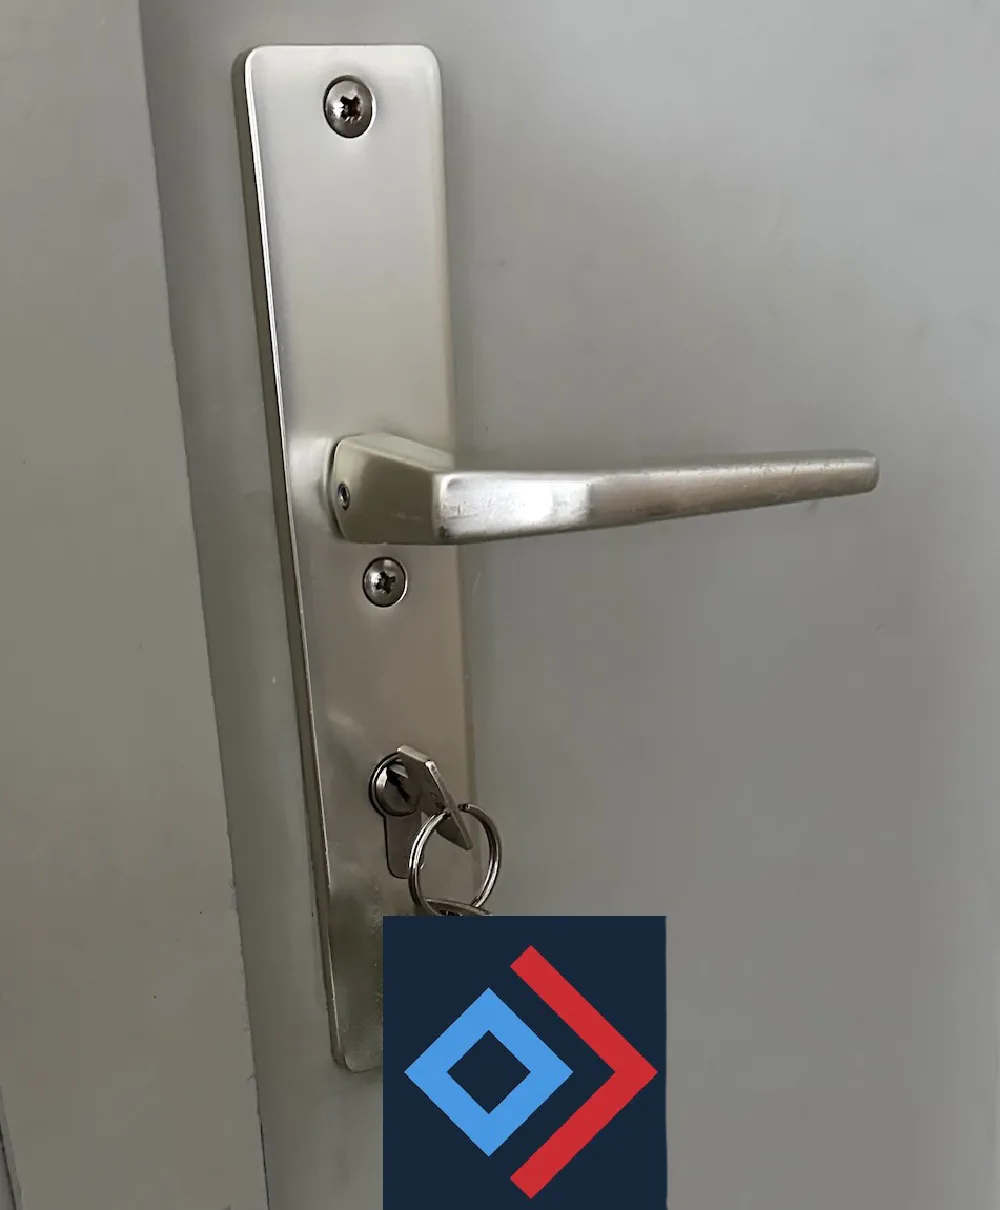
The key is left in the lock from the inside and the cylinder has no copy protection. The door is solid and undone by an everyday oversight.
- Effort: low
- Priority: medium-term
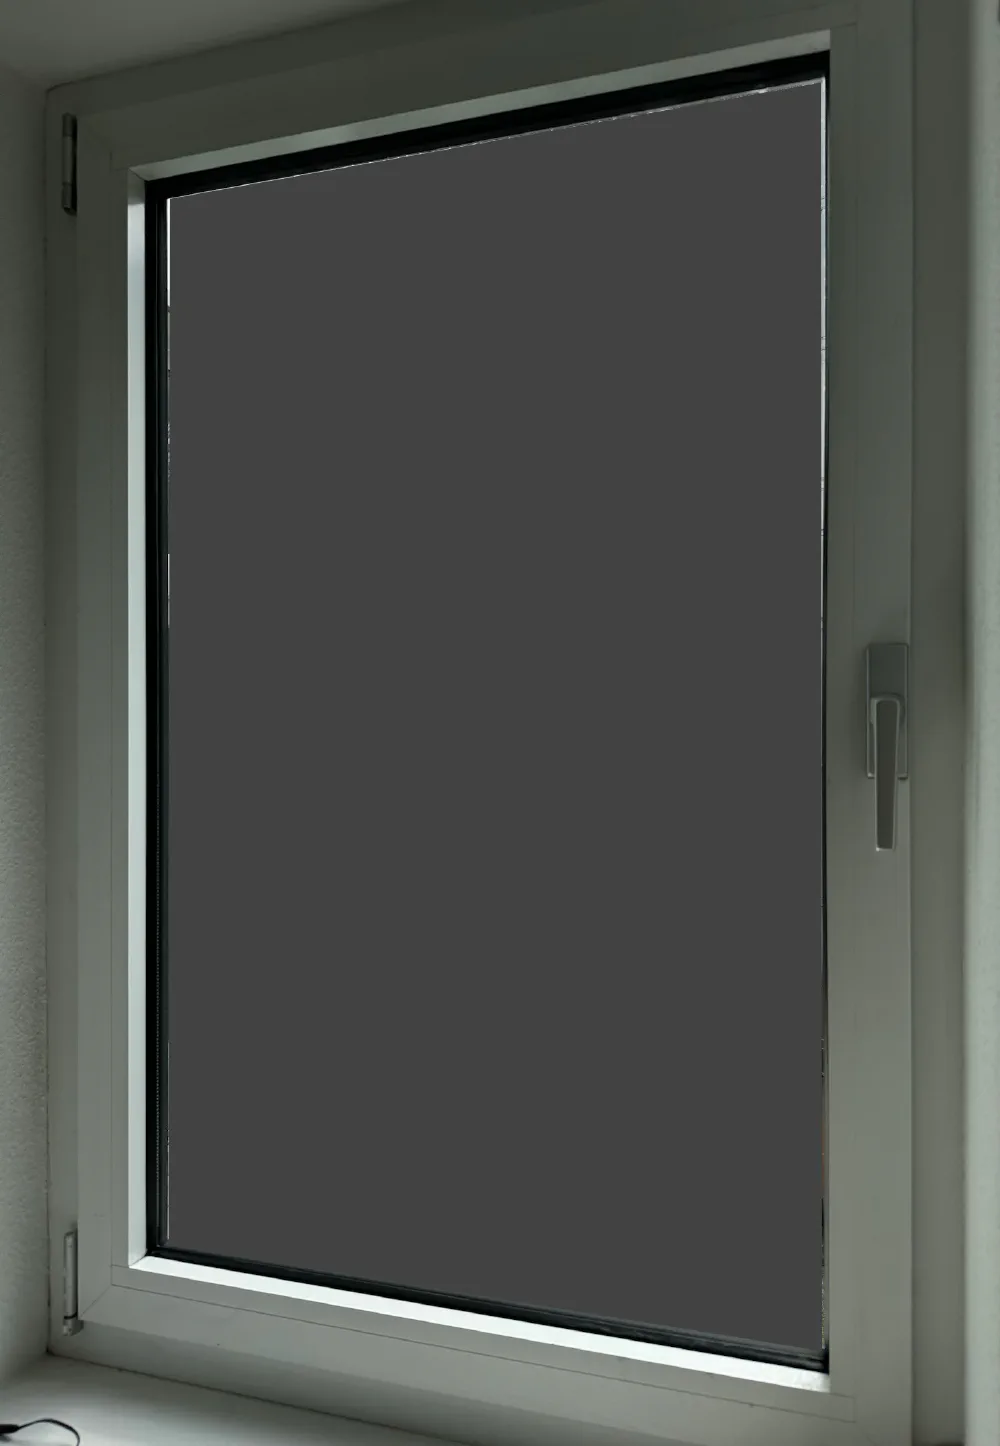
Ground floor, not visible from the street, no burglary protection. After hours this window bypasses the doors and the cameras.
- Effort: medium
- Priority: medium-term
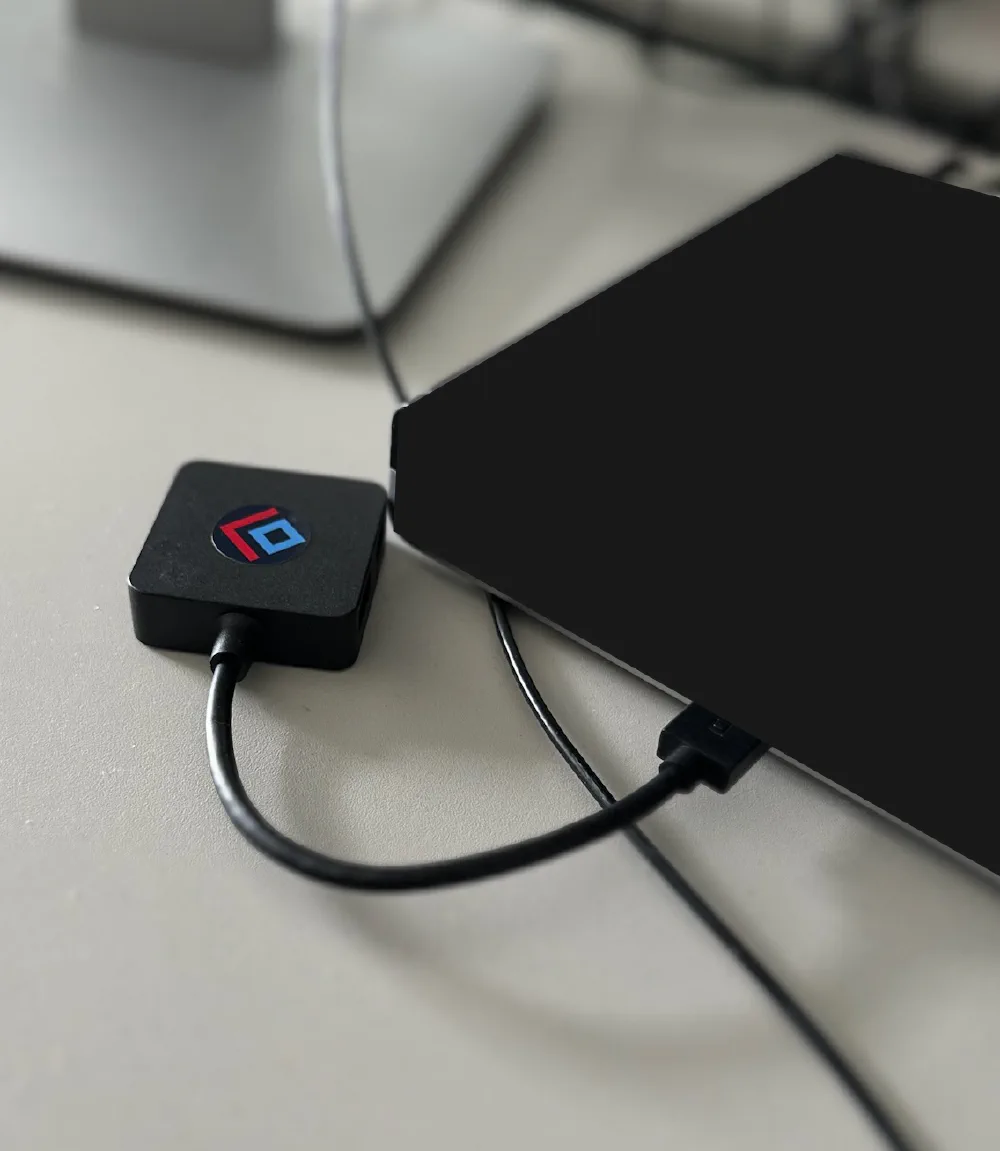
Placed days before the walk-through, clearly visible at the desk. By the end of the audit nobody had reported it.
- Effort: low
- Priority: medium-term
Who tests
Certified for both worlds
Offensive security: OSCP, OSWE and OSEP (OffSec). Physical security: Covert Access Training and Physical Audit Certification by the Covert Access Team, BHE-certified security concept specialist (KRITIS). Plus a top-100 ranking in Intigriti’s bug bounty program and four CVEs of his own.
How we work
Book a call
NDA before every audit
Confidentiality is a precondition. We sign before you show us anything.
Agreed rules of engagement
Scope, limits, emergency contact and time windows are agreed in writing with your management. Your team knows what happens when.
An independent, readable report
One-page summary, photos as evidence, measures in three tiers: immediate, medium-term, investment. It recommends what helps your site most, regardless of who implements it.
In 30 minutes you will know whether a review makes sense for your site.
We listen to how your business works and what would hurt it most. The call is free and without obligation. Call +49 3683 6539040 or book a slot.
Book a call