

Your systems are running. When did they last have to withstand a targeted attack?
Penetration tests for web, API, cloud and internal networks. With several user roles, code review on request, and a report your developers can act on directly.
Book a call- OSCP
- OSWE
- OSEP
- CCSK
Tools for breadth, experience for depth
Automation is part of every test: it covers the attack surface and finds known vulnerabilities fast. What it misses: authorization mistakes, business flows that can be abused, weaknesses that only become a problem across several systems.
That is where we focus, on the points that long experience and current security research make relevant for your system, with several user roles and, if you open the code to us, inside it as well. After more than 15 years of building software we know where such mistakes come from and how to describe them so developers can fix them directly.
What we test
Request a pentest
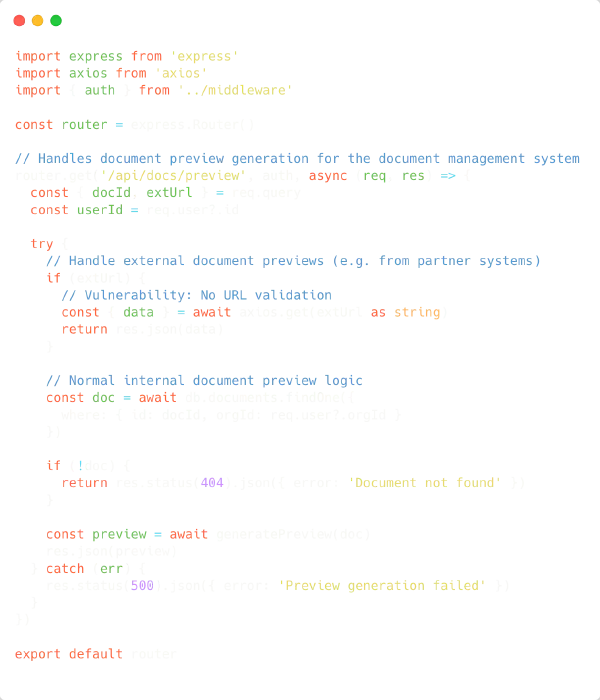
Web applications & APIs
REST, GraphQL, single-page apps, multi-tenancy. With every role, authenticated and unauthenticated.

Cloud infrastructure
AWS and Azure: permissions, storage, serverless, containers and the paths from an application into the environment behind it.

Internal network & Active Directory
What an attacker reaches with a network socket or an ordinary user account: segmentation, privileges, legacy systems.

Code review as an add-on
On request we open the source code (PHP, Java, TypeScript, .NET) and test white-box. Finds what stays invisible from outside, and shows it where it gets fixed.
How a penetration test works
Progress updates during the test, critical findings at once
Brief call
30-45 min.We get to know your systems and business: applications, infrastructure, roles, what an attacker would want. Scope and quote follow from that.
Order & rules
in writingWritten order and rules of engagement: scope, time windows, contacts, emergency contact.
Test
by scopeAutomated for breadth, targeted for depth, with several roles, as a black-box, grey-box or white-box test. Critical findings are reported immediately, while the test is running.
Report
on completionSummary for management, every finding with evidence, rating and a recommendation for the development team
Debrief & retest
includedWalk through the findings together, re-test after remediation and confirm in writing
From the field
Bug bounty as continuous training
Alongside client projects we test large platforms on invitation: 75 accepted findings in more than 15 programs, top 100 on Intigriti, four CVEs of our own. It keeps the methods current without your project being the practice ground.
When the way into the network is through the door
Many attacks do not start on the internet but at a network socket in the hallway or with a device at a desk. That is why every penetration test can be combined with a physical review of your site: one order, one report, one attack path from outside to the data.
What you get
Book a call
Evidence you can rely on
Every finding is reproducibly documented, rated and verified by hand. You get checked results.
Retest included
After remediation we test again and confirm in writing what is closed.
Workshop on request
Walk through the findings with your development team so the next release does not repeat them.
NDA and clear rules
Confidentiality before the first login, written rules of engagement, encrypted delivery of the report.
Which systems should we test?
In 30 minutes we get to know your systems and your business and clarify what should be tested. Then you receive a quote. The call is free and without obligation.
Book a call